


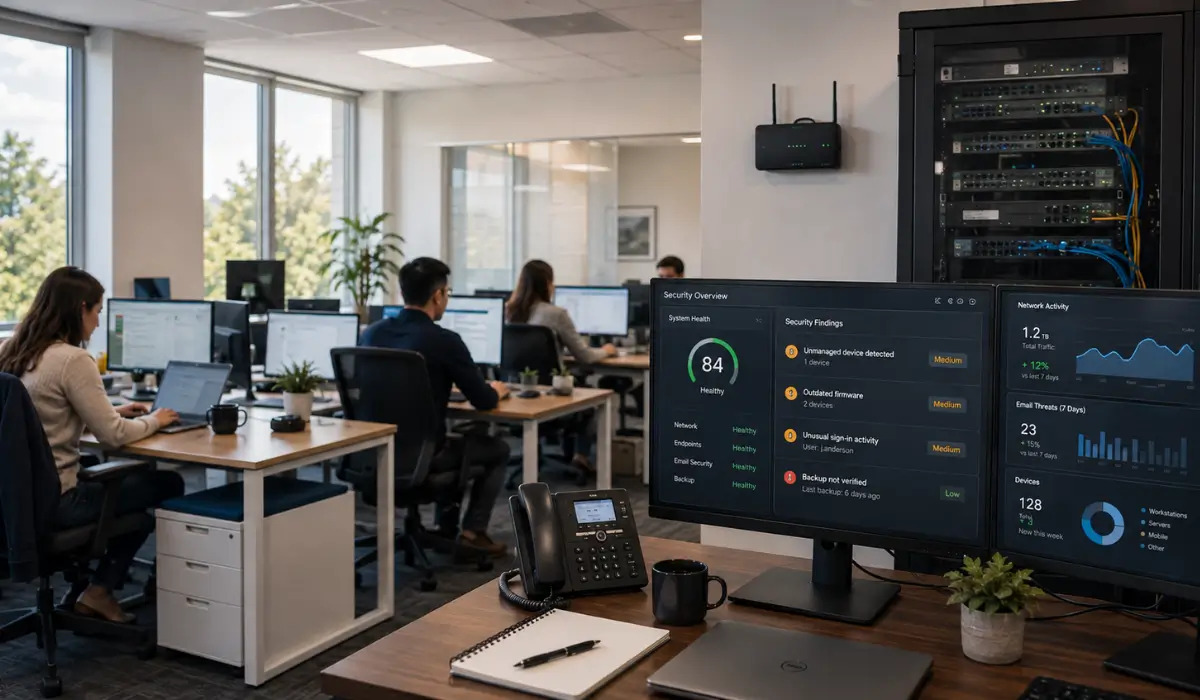
A business network can work normally and still have security gaps. An August IT security audit checks devices, access, backups, email security, monitoring, and other controls so problems can be addressed before they create larger risks.
Working internet, active antivirus, and functioning devices do not prove an environment is secure. Unsupported equipment, unnecessary access, missed patches, and untested backups can remain unnoticed during daily operations.
KubeTech helps businesses in Villa Park and the Chicago suburbs keep technology secure, reliable, and easier to manage. August is a practical time to identify concerns before Q4 planning and year-end work become more demanding.
August gives businesses a useful window between summer schedules and year-end priorities. Budgets are taking shape, projects are being considered, and there is still time to address security concerns before Q4.
August also gives businesses time to strengthen security practices before Cybersecurity Awareness Month in October puts more attention on phishing, access controls, and employee readiness. Some findings require coordination with employees, vendors, or business schedules, so finding them now gives leaders time to plan the right response.
A late-summer review can uncover:
If routine maintenance is already planned, these business downtime prevention tips show how regular upkeep can reduce avoidable interruptions.
Maintenance keeps systems working as expected. A security review looks for weaknesses that could expose those systems or make recovery harder.
A security audit reviews technology, security controls, user access, backups, monitoring, and related processes. It determines whether the environment is being managed securely, not simply whether the equipment works.
An audit is broader than a vulnerability scan. Scanning focuses on technical weaknesses, while an assessment can also review permissions, recovery, employee practices, response processes, and compliance readiness.
A complete review typically covers:
These areas are connected. A firewall cannot remove an old employee account, and a completed backup does not prove critical systems can be restored.
This approach is consistent with the NIST Cybersecurity Framework, which organizes cybersecurity risk management around identifying, protecting, detecting, responding to, and recovering from risk.
A useful assessment should leave leadership knowing what was found, why it matters, and what should happen next.
A thorough IT security audit looks beyond one security product. Devices, accounts, email, backups, monitoring, and employees all affect the overall security of the business.
For each area, three questions matter: What is in place? Is it supported and working as intended? What happens if it fails? These questions keep the review focused on business risk rather than a simple inventory of technology.

Routers, switches, firewalls, and wireless access points should be reviewed for age, configuration, firmware, and manufacturer support.
For businesses evaluating network infrastructure service Villa Park IL, the useful question is not simply how old the equipment is. Documentation, firewall configuration, wireless security, support status, and monitoring all affect how reliably the network can be managed.
Diagnostic question: Can every critical network device be identified and confirmed as supported?
Current equipment records make it easier to plan upgrades before an unsupported or failing device forces the decision.
Employee access changes as people join, leave, or change roles. Old accounts, shared credentials, and unnecessary administrator rights can remain active when access is not reviewed.
Multi-factor authentication adds protection, but it does not replace account cleanup or proper permission management.
Diagnostic question: Does every active account still belong to someone who needs that level of access?
Regular access reviews help keep permissions aligned with current responsibilities instead of past roles.
Laptops, desktops, and mobile devices can create security gaps when patches are missed, protection stops working, or remote devices are not properly managed.
Our managed IT and cybersecurity services include monitoring, patch management, and layered security controls. For businesses researching endpoint security services Villa Park IL, the key question is whether every device can be identified, updated, protected, and managed consistently.
KubeTech works across Microsoft, Google, cloud, network, and device environments. Accurate device records make missed updates and unmanaged endpoints easier to identify.
Email security requires both technical controls and employee judgment. Filtering helps, but employees still encounter login prompts, links, attachments, invoices, and unexpected requests.
Our managed email services include phishing protection, spam filtering, login monitoring, Microsoft 365 backup, and support. Email authentication settings should also be reviewed to confirm the business’s mail environment is configured as intended.
Businesses researching email phishing protection service Villa Park IL should consider account protection, monitoring, employee reporting, and recovery—not only spam filtering.
Diagnostic question: Does everyone know how to report a suspicious message?
Strong email security gives employees a clear response when something suspicious gets past technical controls.
Having backups does not prove a business can recover. What matters is whether critical data and systems can actually be restored after a disruption.
The review should also confirm how quickly critical systems need to return and how long important business data needs to be retained. Those requirements help determine whether the backup and recovery process matches actual business needs.
Every business should be able to answer three questions:
CISA’s ransomware response recommendations include backup and recovery measures as part of ransomware preparation and response.
Recovery testing should account for cloud services, applications, identity systems, and network access. Restoring files alone may not be enough if employees cannot access the systems needed to work.
Monitoring can identify outages, device failures, performance changes, and security events, but collecting alerts is not enough.
Businesses considering 24/7 network monitoring service Villa Park IL should know who receives important alerts, how they are evaluated, and what happens next.
KubeTech combines 24/7 monitoring with maintenance and support so meaningful alerts can lead to a clear response.
Employees make security decisions when they handle passwords, account prompts, invoices, links, and unexpected requests.
Training should prepare them for phishing and social engineering tactics such as impersonation, unusual payment requests, and attempts to obtain credentials.
Diagnostic question: Does everyone know where to report suspicious activity?
Together, these seven areas show whether security controls support one another or leave gaps between people, systems, and processes.
Reviewing them together also helps uncover weaknesses that can be missed when each control is checked on its own. A strong firewall, for example, cannot compensate for unnecessary account access or an untested recovery process.
Security problems do not always start with an outage. Repeated or unexplained activity can signal that the network deserves closer attention.
For businesses researching network security service Villa Park IL, the most useful warning signs are patterns that cannot be explained by normal activity.
Common signs include:
One failed login or slow connection may have an ordinary cause. A repeated pattern that nobody can explain deserves investigation.
CISA includes urgent requests, requests for personal information, and suspicious links among common phishing warning signs. Employees can also use these everyday cybersecurity practices to strengthen daily security habits.
The goal is not to treat every unusual event as an attack. It is to understand normal activity well enough to recognize when something needs investigation.
A technical weakness becomes a business problem when it interrupts operations, exposes information, delays recovery, or creates compliance concerns.
Healthcare, legal, financial, manufacturing, and professional services organizations may also have industry, contractual, or regulatory requirements that affect security priorities. The impact of a weakness therefore depends partly on the systems, information, and obligations involved.
| Risk | Business Impact | Key Question |
|---|---|---|
| Downtime | Interrupted operations | Which systems must stay available? |
| Account compromise | Data exposure | Who has privileged access? |
| Recovery failure | Extended disruption | Has recovery been tested? |
| Compliance gap | Regulatory or contract concerns | Which requirements apply? |
| Reputation damage | Customer trust concerns | Who depends on the affected system? |
Not every technical finding deserves the same response. Priority should reflect exposure, operational importance, and the consequences of failure.
That approach keeps attention on the issues most likely to affect the business rather than treating every technical finding as equally urgent.
An assessment captures conditions at one point in time. The environment keeps changing as employees join or leave, devices are added, software is updated, and configurations change.
Businesses researching network device monitoring Villa Park IL should consider whether those changes remain visible after the assessment.
Monitoring can reveal device failures, security alerts, performance changes, suspicious activity, and unexpected network behavior. Someone must also know which alerts require action and who is responsible for responding.
An assessment establishes a baseline, while continuous monitoring helps identify changes between reviews. Together, they reduce the chance that new security gaps go unnoticed.
Security assessments and penetration tests can both identify weaknesses, but they answer different questions.
A business without reliable device records, access controls, patching, or tested recovery may need to strengthen those basics before specialized testing makes sense. The right starting point depends on what the organization is trying to verify.
Recurring support issues may require ongoing management, while a migration, security initiative, or overloaded internal team may call for specialized expertise.
KubeTech is a family-owned IT services company based in the Chicago suburbs. We help small and midsize businesses manage daily technology needs, cybersecurity, email, communications, and technical projects.
Our technology and cybersecurity team works across Microsoft, Google, cloud platforms, networks, and devices. That range of experience helps us look beyond a single issue and consider how different parts of the environment affect one another.
When comparing a managed IT provider Villa Park IL, look beyond the service label. Consider whether the provider understands your systems, can address your security risks, and is prepared to take responsibility for the areas where you need ongoing support.
To discuss a specific support or technology need, call (630) 534-2300.
| Security Assessment | Penetration Test |
|---|---|
| Reviews systems and controls | Simulates defined attacks |
| Considers people and processes | Tests technical attack paths |
| Identifies gaps and priorities | Tests exploitability |
| Supports broad planning | Supports focused testing |
Larger corrections can be handled through IT infrastructure project services, including network upgrades, cloud migrations, and infrastructure improvements.
Neither approach is automatically better. The right choice depends on the risk or question the business needs to investigate.
Business leaders do not need to manage every security control themselves. They do need enough visibility to understand risk, recovery readiness, and responsibility.
An IT security audit should help leadership answer:
If several answers are unclear, that uncertainty deserves attention.
Businesses connecting technical priorities with budgets and future plans can work with our IT and cybersecurity specialists. For organizations considering IT consulting Villa Park IL, the value is in turning individual technical concerns into clear priorities, budgets, and next steps.
A good review ends with clear ownership: what needs action, who is responsible, and when the result will be verified.
Finding a weakness has limited value if nobody knows what happens next. A practical process moves each important finding from identification to verification.
Technical complexity and business risk are not the same. A simple access problem can create more exposure than a complex issue affecting a low-priority system.
The result should be a clear list of priorities, owners, and next steps—not simply a longer list of technical problems.Lorem ipsum dolor sit amet, consectetur adipiscing elit. Ut elit tellus, luctus nec ullamcorper mattis, pulvinar dapibus leo.
The right level of support depends on company size, systems, employee access, compliance needs, and internal resources.
Businesses comparing cybersecurity services Villa Park IL should look for support that connects daily technology needs with security and longer-term planning.
Some businesses need responsive support and monitoring. Others may need stronger security controls, infrastructure work, or long-term technology planning. More tools do not automatically mean better protection.
Our business IT services bring support, security, and planning together for small and midsize businesses. The right arrangement should address real risks without adding unnecessary complexity.
A security assessment should result in usable priorities, not a report that sits untouched. The business should know who owns the work after a weakness is identified and how the correction will be checked.
Two questions reveal a lot about the process:
Identifying a weakness, making a change, and verifying the result are separate steps. Businesses should also know who responds to alerts, how priorities are ranked, and whether recommendations account for schedules and budgets.
Clear ownership reduces the chance that an important finding remains unresolved after the assessment. It also helps leadership understand which work needs immediate attention and which improvements can be planned.
The practical test is simple: after a problem is identified, does everyone know what happens next—and how success will be checked?
A late-summer security review makes sense when the business cannot confidently answer questions about access, backups, monitoring, equipment support, or response ownership.
That does not mean a major project is automatically needed. One business may need account cleanup and recovery testing, while another may need to replace unsupported network equipment.
A current firewall, for example, does not offset an unnecessary administrator account. Likewise, well-managed access does not remove the risk created by unsupported equipment.
Assess first, understand the risk, then decide what needs to change. Security spending should follow evidence rather than assumptions.
An IT security audit should show what needs attention now, what can wait, and what is already working well. The goal is a practical security plan—not unnecessary tools or spending.
KubeTech helps Villa Park businesses identify meaningful risks and choose the right next step based on their systems and business needs.
Prefer to talk through your concerns first? Call (630) 534-2300.